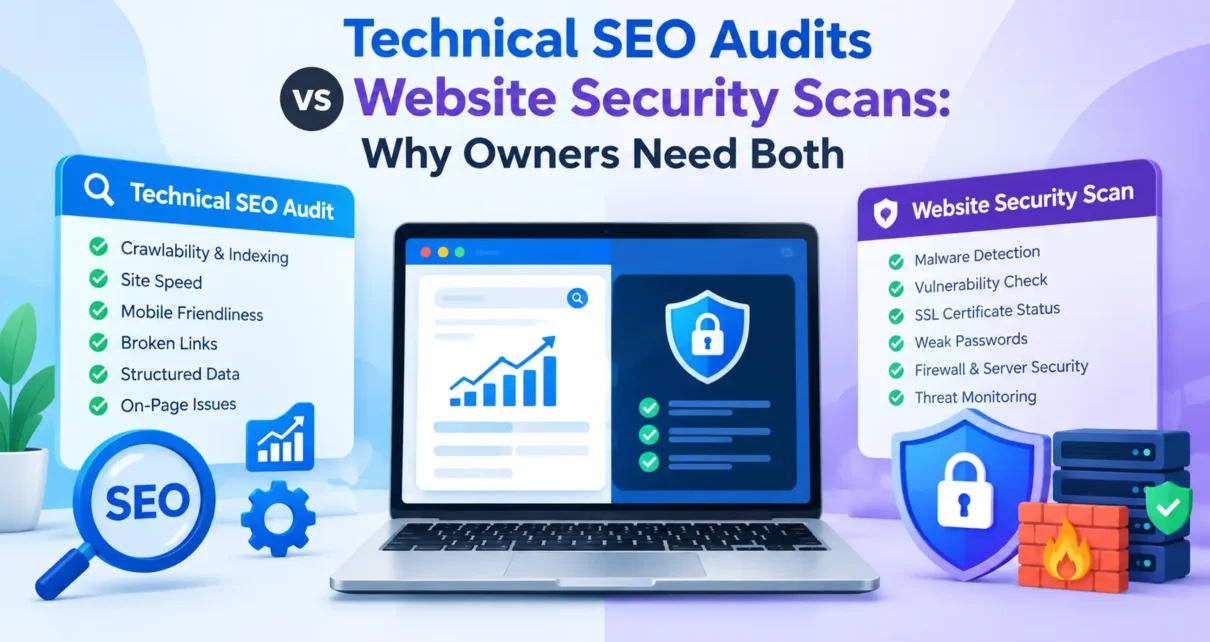
Most site owners run one of these and not the other. Marketing teams run SEO audits; developers run security scans; each assumes the other covers whatever they do not. In practice the two overlap on several checks, diverge sharply on others, and the gap between them is where the expensive problems live.
Where they genuinely overlap
Several items appear in both reports, for different reasons:
| Check | Security reason | SEO reason |
|---|---|---|
| HTTPS everywhere | Prevents interception and tampering | Confirmed ranking signal; browser warnings kill conversions |
| Valid certificate | Trust and encryption | An expiry warning stops crawling and traffic outright |
| Redirect consistency | Avoids downgrade paths | Prevents split indexing across protocol and host variants |
| Mixed content | Weakens page integrity | Blocked resources mean incomplete rendering |
| Page speed | Often reflects unpatched stacks | Core Web Vitals |
| Exposed directories | Information disclosure | Thin pages indexed, crawl budget wasted |
That last row is worth dwelling on. An exposed backup directory is a security finding and an SEO one: search engines will happily index a directory listing, and staging copies indexed alongside production create duplicate content at scale.
Where a security scan sees what an SEO audit misses
- Injected content. Compromised sites frequently serve spam links only to search-engine user agents. Your SEO tool crawling as itself sees a clean page.
- Vulnerable plugins and libraries. No SEO impact until the day there is a very large one.
- Missing headers and cookie flags. No ranking effect; the difference between a contained incident and a serious one.
- Email authentication. SPF, DKIM and DMARC records determine whether someone can convincingly spoof your domain. Nothing to do with rankings, everything to do with brand trust.
A security headers checker takes seconds and covers a category most SEO tooling does not report on at all.
Where an SEO audit sees what a security scan misses
Canonicalisation, internal linking, redirect chains, structured data, hreflang, index bloat, crawl budget, thin and duplicate content, title and description quality. A security scanner has no opinion on any of it, because none of it is a security property. Crawling for those issues is what an SEO audit is for.
The gap that costs the most
The scenario that damages sites badly sits between the two disciplines: a site is compromised, injected content is cloaked to search-engine crawlers, rankings degrade over weeks, and the marketing team investigates as an SEO problem while the developers see nothing because the site looks fine in a browser.
Three symptoms that should immediately trigger a security check rather than more SEO analysis:
- Indexed pages you did not create, especially in languages you do not publish in.
- A sudden ranking drop with no algorithm update and no site changes.
- A manual action or a “this site may be hacked” label in search results.
In all three cases, fetching the page as a search-engine user agent and comparing it with what a normal browser receives is the diagnostic. If they differ, you have a security incident wearing an SEO costume.
A workable cadence
| Frequency | Do |
|---|---|
| Weekly | Automated security scan; check for indexing anomalies |
| Monthly | Crawl for SEO issues; review certificate expiry |
| Quarterly | Full technical audit; dependency review |
| On any change | Both, after a migration, redesign or CDN change |
The two reports answer different questions — “can this site be found and understood” and “can this site be trusted and left alone”. Running only one leaves the other unanswered, and the unanswered one tends to be the one that eventually costs money.